Activity
Mon
Wed
Fri
Sun
Dec
Jan
Feb
Mar
Apr
May
Jun
Jul
Aug
Sep
Oct
Nov
What is this?
Less
More
NavAIgate AI Agents & Harness
65
5.0
$79/m
Autonomee
221
$102/m
Build Market Close
790
5.0
Free
Lead Gen Insiders by LGJ
2k
$1,497
AI INSIDERS 👨🏻💻
6k
Free
Clief Notes
55.5k
5.0
Free
AI Automation Agency Hub
337.6k
Free
The RoboNuggets AI Network
109.8k
Free
Maker Zero: Claude Code, AI
44.4k
Free
35 contributions to Build Market Close

2d •
What video do you NEED for your business?
Hey everyone! @Ry Mac asked me if I could make some videos for the group, so before I build anything I want to know what would actually help you. The video shows what I've made so far. Watch it for ideas, then vote. And in the comments: if you could have one video made in 5 minutes, what would it be about?
Poll
6 members have voted

3d •
1 Folder AI Operating System Course Launching Soonz
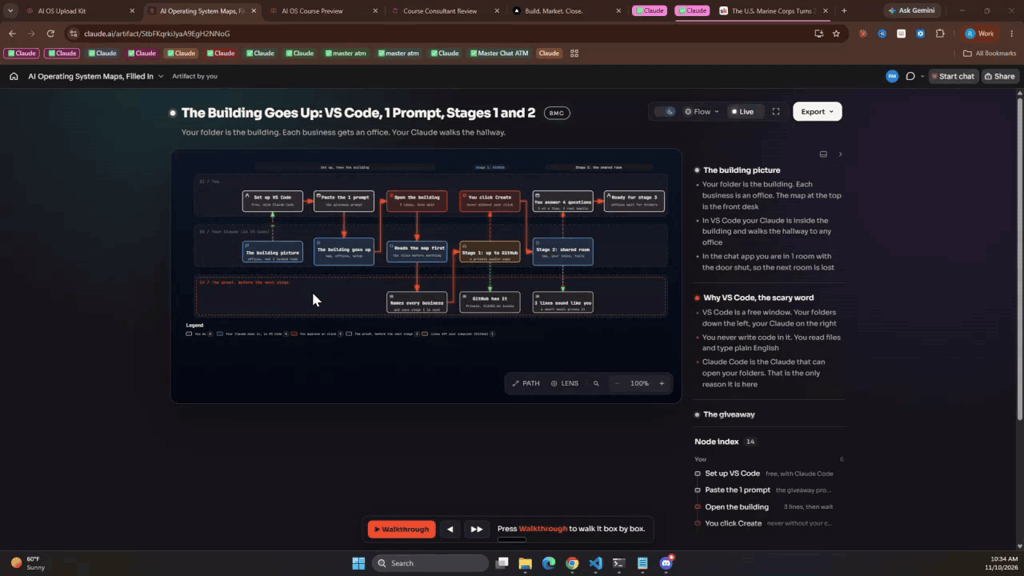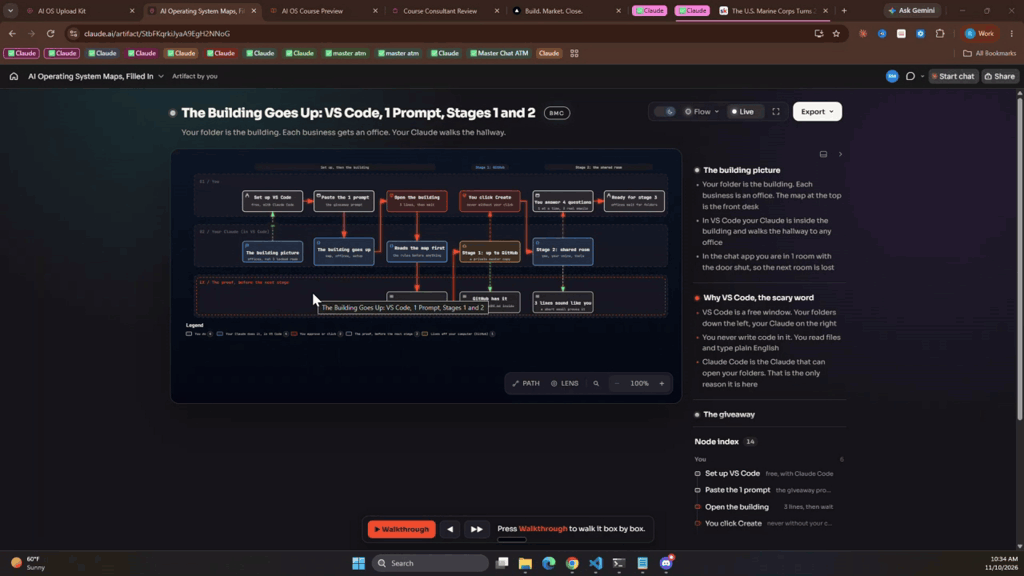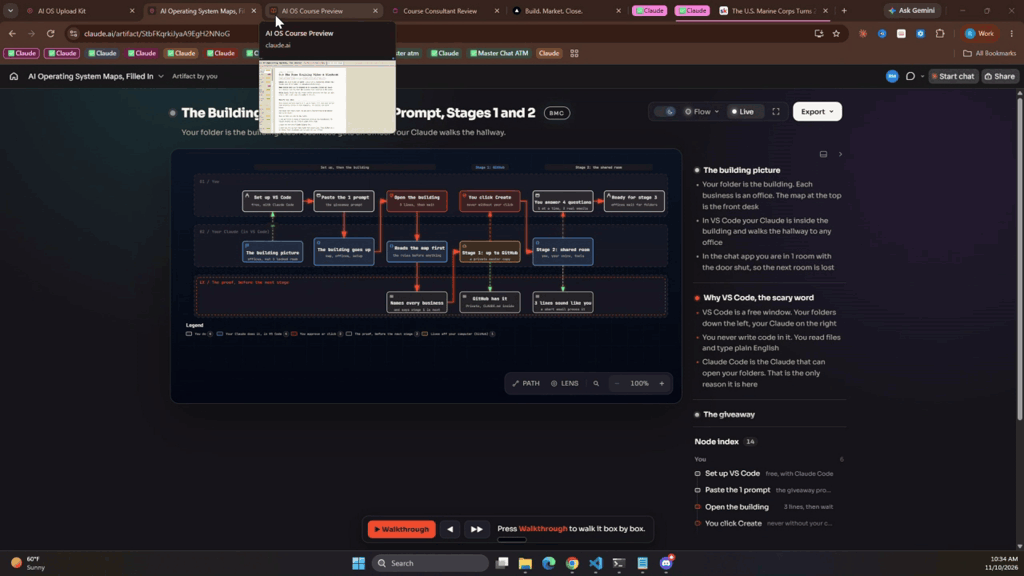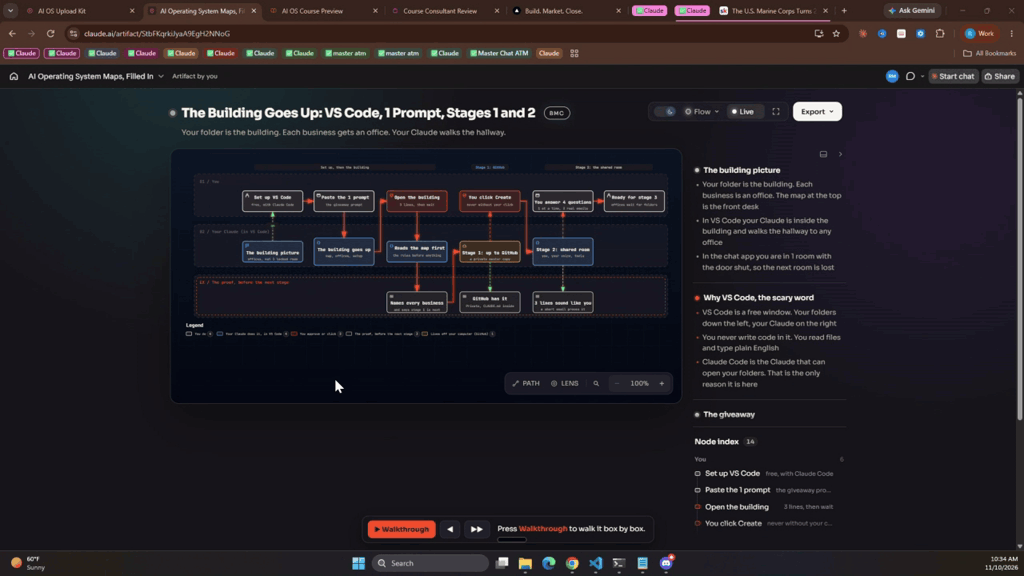
So... I have been launching content out into "buckets" -Building -Marketing -Closing -ICM Nothing truly structured. Just a topic, thrown into a bucket, some zip files for you to point your AI at and "go". This week, that changes... I'm launching a structured course on how to set up you 1 Folder AI Operating System. The end result is your own AI operating system built in 1 folder, the same way you've seen me operate mine. It has 84 micro lessons over 11 sections, each lesson ends with an action for you to take. For the most part each lesson can be finished in 5'ish minutes. It's baby steps so that you can learn things the right way. The why, the idea, the real life example, and your practical app. The BMC platform is 95% done as well (shown in video). Note* - I mentioned GSD being used on the BMC build (and all of my apps moving forward) repo is here: https://github.com/open-gsd/gsd-core I highly recommend my vibe coding frens' check it out. Shot ya a quick video 👇
3 likes • 3d
[attachment]
7d •
Customers vs. Clients
A lot of people get this confused. I see people routinely refer to customers and clients as if they're they same and they're not. This is my short take: - A customer buys a product or service from you that works without you - A client buys your (or someone on your teams) time and you work with them People think they want to start an "AI agency" and they want clients but they do not realize the ability to scale a client based business is much harder and more expensive than "gurus" will tell you. Then they close some deals and realize they've created their self another J.O.B. and not a business. You're replacing time for money. A business that has customers is much easier to scale with hiring margins and less overhead. You're providing a solution that you spent your time on building. It doesn't trade your time for money. This is easier to scale. Neither business model is wrong or right, it's just wrong or right depending on what it is you actually want to do vs what it is you think it does. An example: My VIP has clients (we meet weekly and I'm trading time for money ) My Perfect ICM Builder has customers (we never speak and I'm not trading time for money) So let me ask you... Do you want customers or clients? Lemme' know below 👇
Poll
18 members have voted

1 like • 3d
@Ry Mac I want actually both, but in the right proportion. I enjoy client work, and customers are a great way to provid high value without exchanging time for money.
4d •
Ran the 4R audit on my whole workspace. My guards work, they just weren't getting called
Ran the 4R audit on my whole workspace. My guards work, they just weren't getting called. I was out all weekend so I'm catching up today. Glad I did it. Context: I run everything out of one folder, ~/OS, about 219k files. Customers, services, a Telegram bot, Spanish outbound for some of my clients, around 30 hooks I built to keep the agent honest. I ran 4R v1.5.3 on the whole thing, did one fix pass, then re-audited the same day. What it found that I would never have found myself: 1. My Spanish proofread gate was blind on 3 of 4 send routes. I moved all my Gmail to Composio a few weeks ago. The gate still only watched the old Gmail tools. So a Spanish email to a customer could go out with no proofread at all. The hook was fine. The wiring wasn't. 2. A leftover "proofread passed" marker had been sitting in /tmp for over 2 hours, with no age limit. The next Spanish send would have gone straight through. It's good for 15 minutes now. 3. 6 of my rules lived only as a sentence in a context file. Planted tests went right past every hook. Supabase GRANTs, no new files in the root, date prefixes on file names, things like that. 5 of the 6 are hooks now. 4. The cold walk was the best part. A fresh agent with no context got stuck exactly where my files contradicted each other (my root file said meeting action items live per customer, the skill still wrote them to one central file). I would have sworn that was fixed. 5. 7 repos had commits that never reached GitHub, including my whole .claude folder with no online copy. That one hurt a bit. something to point out: the planted tests are saved, so the next audit replays them first. 48 of 48 hold today. If I break a guard next month, I'll know.

1 like • 4d
Two small things for you @Ry Mac , on macOS: - `secrets.sh` prints `sed: extra characters at the end of q command` on every hit. BSD sed doesn't like `{p;q}`. - On 219k files it ran well over 10 minutes. Worth a heads up for people with big folders.
9d •
Let's get creative... Handing the least "AI" problems to Claude!
Yesterday I saw video about creative ways to use Claude. Someone connected an old iPad to Claude and repurposed it as a home controls touch screen, someone else connected it to their car!! I was already doing some of that: it solved my house wifi problem and got my 3D printer working remotely. Today I tried a new one. My Mac was down to 90 GB free out of 460 GB, and nothing I could see explained it, so I asked Claude Code: "check my hard drive, which large files can we delete?" It found 236 GB of caches and leftovers; we deleted most of this Free space now: 175 GB... I was able to free up about 85 GB!! What's the least "AI" problem you've handed to Claude?

1-10 of 35